In 2026, loading speed must meet the Doherty 400ms threshold, where clean code and server caching completely outperform heavy plugins. Learn more in our Website Speed Optimization guide.
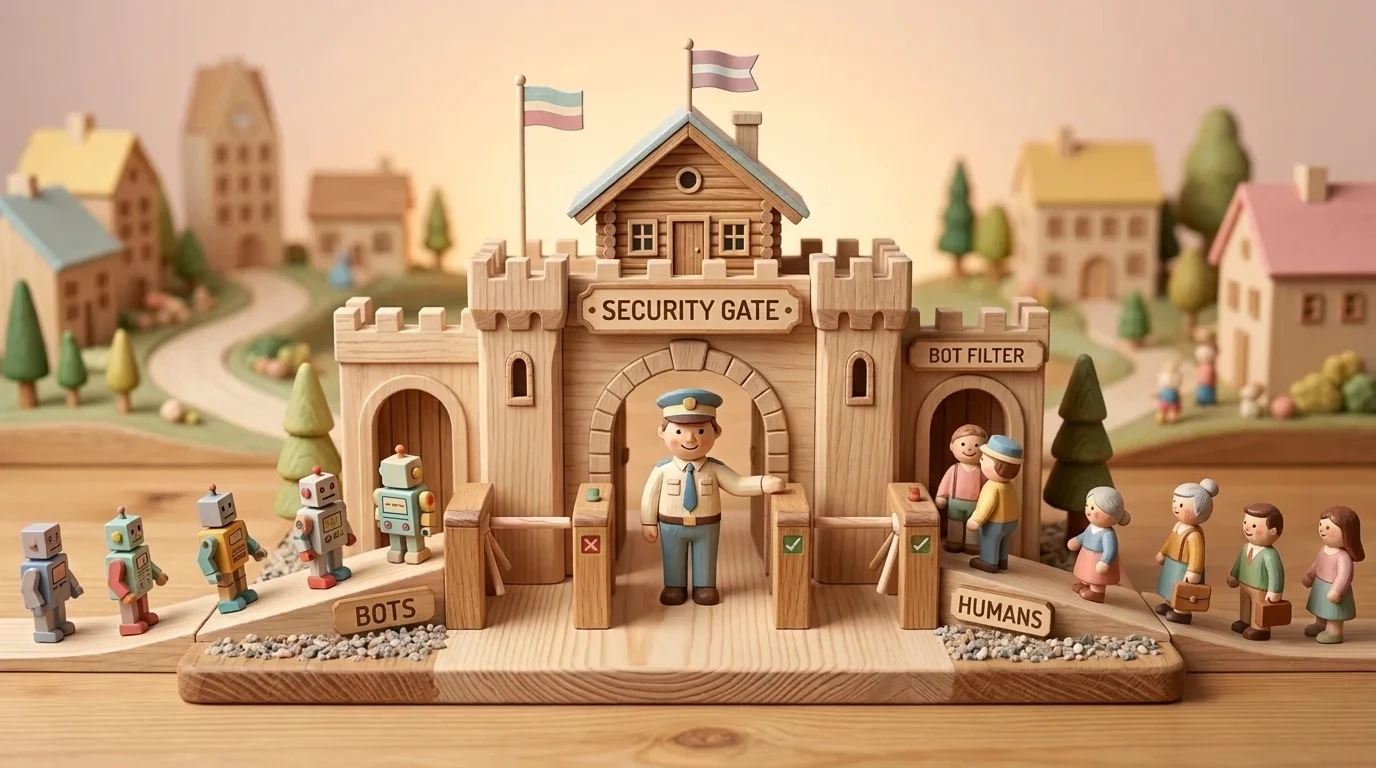
More than 40% of internet traffic consists of bots ranging from harmless search engine crawlers to aggressive content scrapers, fake ad clickers, and password guessers. Without a web application firewall (WAF) and server rate-limiting protection, these attacks slow down your site performance, distort analytics data, and jeopardize website availability.
Today, over 45% of all global internet traffic is generated not by real humans, but by automated bots, scrapers, brute-force attackers, and malicious scanning programs. Business websites in Latvia experience thousands of bot requests every day attempting to crack administrator passwords via wp-login.php, scrape product catalogs with pricing data, or flood contact forms with cryptocurrency spam.
The load generated by these bots not only increases server costs and distorts marketing analytics in Google Analytics 4, but can also completely paralyze website operations during critical moments. A stable and professional server maintenance and security system includes a complete defense architecture without heavy and expensive security plugins.
Step 1 - Blocking XML-RPC and wp-login.php at the Server Level
These risks are completely eliminated by clean code architecture offered by our vulnerability-free web development, disabling outdated XML-RPC at the server level. Through a single XML-RPC request, an attacker can test hundreds of password variations while bypassing standard login limits. This file must be disabled entirely directly within the Nginx server block:
# Block access to XML-RPC for all requests
location = /xmlrpc.php {
    deny all;
    access_log off;
    log_not_found off;
    return 403;
}

# Limit login request frequency (Rate Limiting)
limit_req_zone $binary_remote_addr zone=login_limit:10m rate=2r/m;

location = /wp-login.php {
    limit_req zone=login_limit burst=3 nodelay;
    include fastcgi_params;
    fastcgi_pass unix:/run/php/php8.2-fpm.sock;
}
"Many companies install heavy security plugins like Wordfence, which compare every incoming request at the PHP level. But if you are attacked by a thousand bots per minute, PHP and MySQL themselves collapse from this comparison. Security filters must be positioned right at the front - at the Nginx server level or cloud CDN layer - preventing bots from even touching your code."
Step 2 - Form Protection Without Annoying CAPTCHAs
Users hate traditional Google reCAPTCHA challenges that require searching for traffic lights and crosswalks. This significantly reduces real customer conversions. A better approach is combined protection:
- Honeypot Method: A hidden input field is added to the form (e.g., "Phone 2"), which humans cannot see, but bots fill out automatically. If the field is filled, the submission is silently rejected.
- Cloudflare Turnstile: A modern, lightweight solution that analyzes browser behavior within milliseconds in the background without requiring any user action.
3. Types of Bot Attacks and How to Prevent Them
To verify your website protection, request a comprehensive security and technical code audit and review the summary below:
| Attack Type | Business Impact | Solution |
|---|---|---|
| Brute-force (Password guessing) | Server overload, hacking risk | Disable XML-RPC, 2FA, IP Rate Limiting |
| Form Spam | Cluttered CRM, wasted SMS credits | Honeypot fields, Cloudflare Turnstile integration |
| Price and Content Scraping | Data theft, server CPU load | User-Agent filters, CDN WAF rules |
| DDoS Traffic Spikes | Complete website unavailability | Cloudflare Under Attack mode, FastCGI cache |
Website Security Checklist
/xmlrpc.php returns a 403 Forbidden error.Frequently Asked Questions About Website Cybersecurity and Protection
What is a Web Application Firewall (WAF) and why is it needed?
A WAF analyzes every incoming request before it reaches your server, automatically blocking SQL injections, XSS scripts, and known malicious bot networks.
How to protect the WordPress admin panel from password guessing (brute-force)?
Restrict wp-login.php access by IP address, implement two-factor authentication (2FA), and install Fail2ban at the server level to block IPs after 3 failed attempts.
Is the Cloudflare free plan sufficient for protection?
For basic DDoS protection yes, but a serious business website requires precisely configured Nginx security headers, regular isolated backups, and server monitoring.
Want lightning-fast website loading and green zones in Google PageSpeed tests?
Schedule a 15-minute consultation. We will perform a detailed code and server audit, freeing your site from slowing plugins and libraries.
Fixed budget. No hidden extra charges or forced services.